IgniteIt Cybersecurity is a trade publication covering the business of cybersecurity: the vendors, buyers and capital shaping how companies defend themselves, and what it costs them when they don’t.
What we cover
Security is one of the few budget lines that keeps growing when everything else is cut, and one of the most crowded markets in technology. Thousands of vendors sell into a few thousand serious buyers, and every one of those buyers is being told a different story about what to consolidate, what to replace and what is about to be breached.
Most security media is written for practitioners: the exploit, the patch, the indicator of compromise. That work matters, and plenty of people do it well. Very little is written for the people who decide what gets bought, who gets hired and where the money goes.
We cover five beats:
- Capital — funding rounds, M&A, IPOs, consolidation, and what they say about who is winning.
- Regulation — SEC incident disclosure, CISA, NIS2 and DORA, state privacy laws, and enforcement.
- Market — budgets, pricing, platform consolidation, vendor share and what buyers are actually paying.
- Threats — breaches, ransomware and exploited vulnerabilities, covered for their business cost rather than their technical detail.
- Talent — CISOs, hiring, layoffs, compensation and who reports to whom.
Who we read for
A list of categories is out of date the week it is written, because this industry keeps reorganising itself. We use a three-part inclusion test instead.
- Does the business sell security, buy it at scale, or finance the companies that do?
- Is the reader responsible for a budget, a P&L or an investment decision?
- Would this reader act on a story about security spending, regulation, capital or vendor pricing?
All three yes, or out.
The third test does the work. It is why we do not publish exploit walkthroughs, threat-actor gossip or product reviews: a buyer cannot act on most of it. It is also why we cover things that look technical and are not, like a new disclosure rule, a cyber-insurance repricing or a platform vendor buying a point product. Those land on a budget.
Why we are building this
Security buyers make large, long-lived decisions with very little shared data. Nobody publishes what a mid-market company actually spends on security per employee, what a SOC costs to run in-house against outsourcing it, or what multiple a security platform trades at once growth slows. We intend to.
Who publishes IgniteIt Cybersecurity
IgniteIt Cybersecurity is published by IgniteIt Inc., an events and media company. We have done this before in another fast-moving industry: IgniteIt built a cannabis market intelligence platform alongside the Cannabis Capital Conference, on the premise that information asymmetry is the defining problem of a young market and that the people closest to the deals should not be the only ones who can see them. IgniteIt Cybersecurity is part of the IgniteIt network, alongside IgniteIt Cannabis and IgniteIt Wellness.
Founders
Chairman & Co-Founder
Founded Benzinga, the Detroit financial media company that grew to more than 25 million readers a month.
CEO & Co-Founder
A decade leading revenue strategy, partnerships and event-driven media across finance, fintech and emerging industries.
President & Co-Founder
Leads IgniteIt’s events strategy. Rose from business development at Benzinga to Senior Vice President before co-founding IgniteIt.
Operations
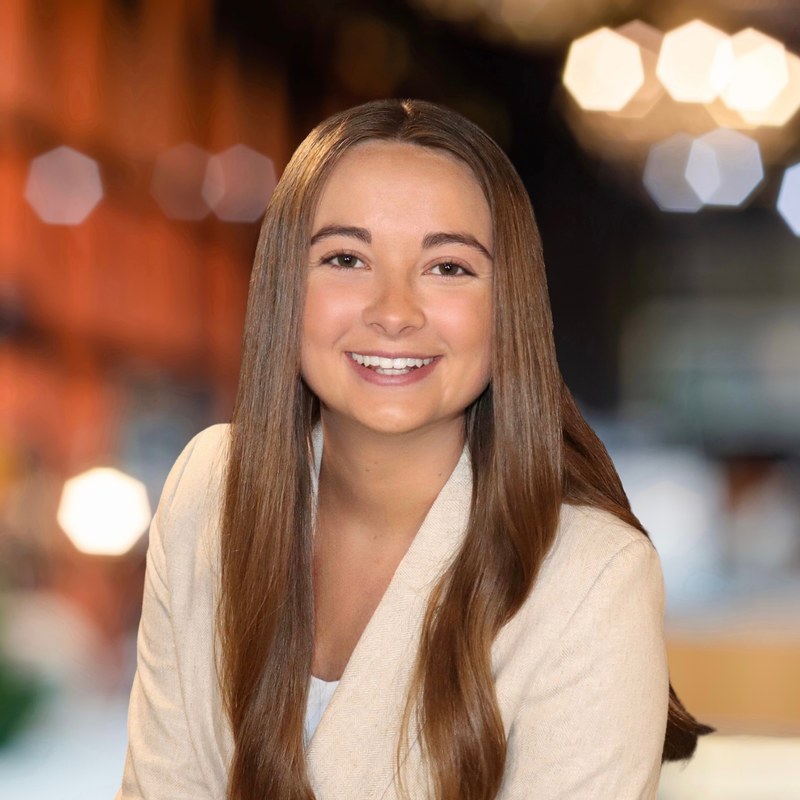
Cori Sickman
Operations Manager
Runs registration, ticketing, vendors and venues across IgniteIt’s conference series.
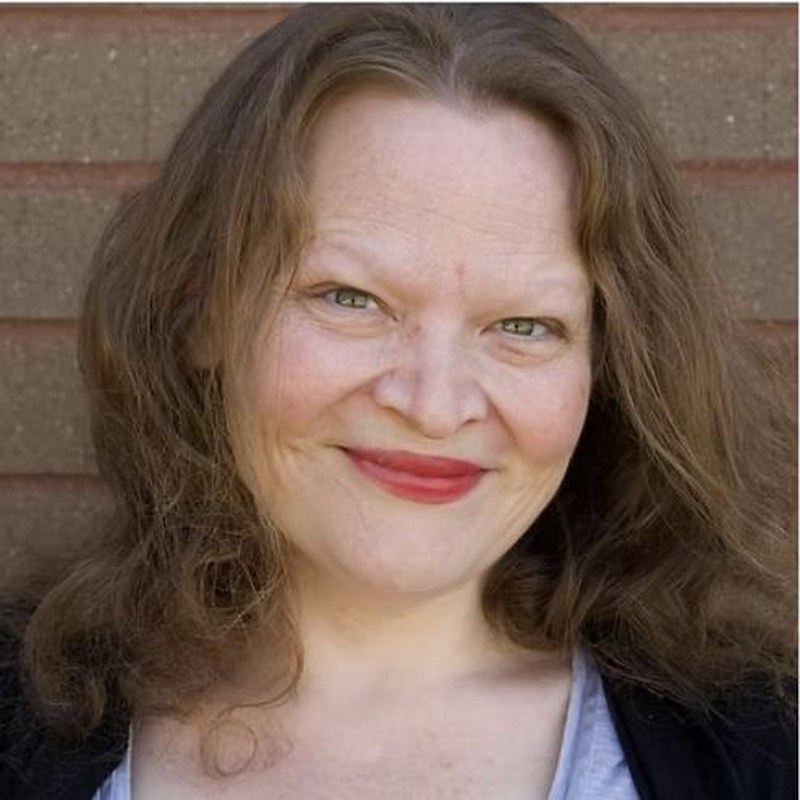
Emily Lehmann
Event Manager
Minnesota-based event manager and former client relations lead at Benzinga.
Every article carries the name of the person responsible for it. See our authors and our Editorial Policy.
What we are not
We are not a threat-intelligence service or a vulnerability advisory. Nothing here replaces your own security team, vendor or incident responder, and nothing here is legal advice. We are also not an investment publication. Nothing here is investment advice.
Get in touch
Story tips, corrections, data submissions and commercial enquiries: see Contact. Our editorial standards, including how we use AI tools, are set out in our Editorial Policy.